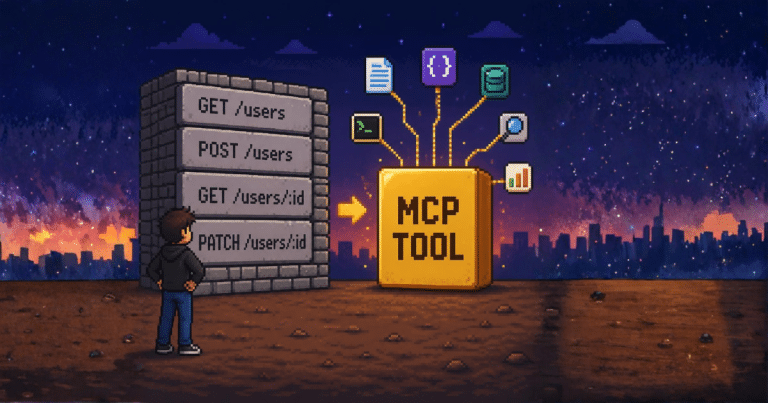
We make many mistakes with MCPs, but one of the biggest is treating them like a 1:1 REST API mapping - when in reality, an MCP tool should be a capability, not just another endpoint.
Anyone who’s clicked "always allow" on an agent knows the outcome: broad permissions, minimal oversight, and results that are correct on paper but strange in practice.
This team was shipping production code at the same time as the MCP specification was taking shape. That is the reality of working with a technology that was evolving in real time.
AI moves faster than your last commit - and so do hackers. Security can’t be an afterthought; it has to run alongside your code, like invisible, always-on seatbelts keeping users safe.
5G was never just about faster speeds. It promised ultra-low latency, edge computing, and smarter connectivity. Sounds perfect, right? Except for one minor hiccup: developers couldn’t access any of it. That’s finally changing.
Let’s be real - getting a call from an unknown number is often just plain annoying. You’re not alone if you hit "decline" right away; around 78% of people do the same to dodge spam or scams. But what if your app could change that experience entirely?
StackOverflow users who have been deleting their contributions since the company announced its API partnership with OpenAI have been temporarily banned and warned not to delete content after they're back.
> subscribe shift-mag --latest
Sarcastic headline, but funny enough for engineers to sign up
Get curated content twice a month
Written by people, not robots - at least not yet. May or may not contain traces of sarcasm, but never spam. We value your privacy and if you subscribe, we will use your e-mail address just to send you our marketing newsletter. Check all the details in ShiftMag’s Privacy Notice